I build and run IT infrastructure architecture.

Focus areas AI architecturesautomationinfrastructure planningproject managementIT audit and DORA

For public authorities, health insurers, banks, energy and industry. Accountability from the architecture decision through to running production: on-premise AI, multi-cloud platforms, Active Directory and ITSM.

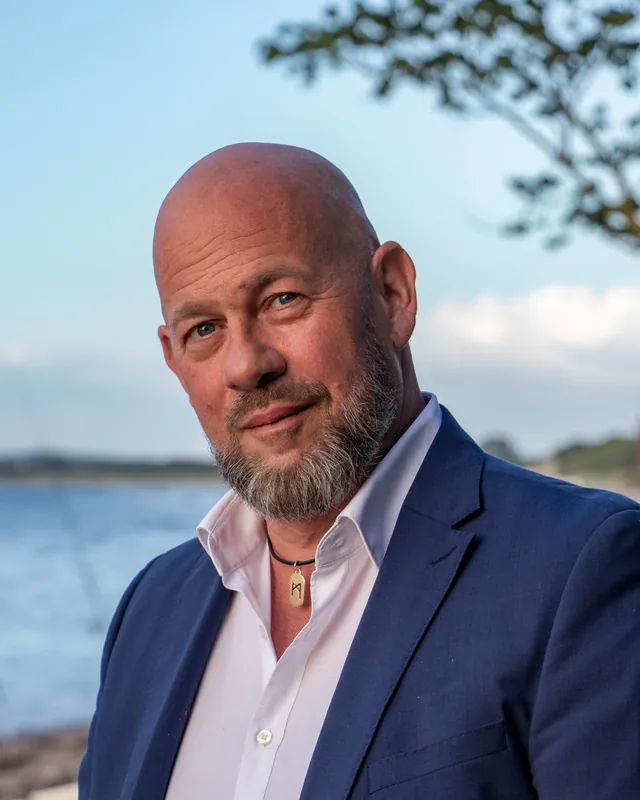
Matthias Barth, portrait
Experience
over 25 years
Documented projects
17
Setting
Regulated and critical
  • VS-NfD
  • KRITIS
  • BSI
  • ISO 27001
  • BaFin
  • C5
  • NIS2

Services

Services at a glance

Six packages, each with a defined outcome and a named handover. Every package is described in detail: starting point, deliverables, duration and what is not included. For regulated organisations, IT audit and DORA is the usual entry point.

Package 1

Architecture review

A defensible assessment of your architecture with a prioritised action list.

Process
Inventory, assessment against target architecture and regulation, prioritised actions, closing session.
Result
Report with prioritised actions, target architecture sketch, decision paper for management.

Package 2

Project and sub-project management

One accountable person for plan, technology and communication.

Process
Scope agreement, planning and work packages, steering team and suppliers, status reporting, handover.
Result
defensible plan, status reports, accepted work packages, documented handover.

Package 3

Interim: lead architect / platform operations lead

The role is filled while you recruit – evidenced by leading a platform team.

Process
Onboarding, technical leadership, weeklies, escalations, architecture decisions, orderly handover.
Result
running operations, decided architecture, documented handover.

Package 4

AI architectures and automation

Run AI in your own network and automate processes – compliant with your rules.

Process
Legal and requirements framing, hardware and platform decision, build and integration, tool assessment, operations handover.
Result
running model operations in your own network, documented operating processes, approved tools.

Package 5

IT audit, DORA and ICT risk management

Become audit-ready: ICT risk management under Article 6 DORA, evidenced and traceable.

Process
Audit planning and scoping, review of the ICT risk management framework, register of information and contracts, findings and remediation tracking.
Result
audit report to IIA and DIIR standards, remediation plan with owners and dates, defensible evidence.

Package 6

Training and seminars

Your team can do it themselves afterwards – in IT, ITSM, project management, cloud, security and DORA.

Process
Tailoring to your environment, materials and practice environment, delivery using your own cases, wrap-up with proof of learning.
Result
trained team, reusable materials, exam preparation for ITIL, PRINCE2 or ISACA on request.

Services in detail Opens all four packages in a window over this page. Escape closes it again.

Closes the window. Escape does the same; focus returns to the link that opened it.

Services

Services at a glance

Six packages, each with a defined outcome and a named handover. Every package is described in detail: starting point, deliverables, duration and what is not included. For regulated organisations, IT audit and DORA is the usual entry point.

Package 1

Architecture review

For organisations whose IT grew over years and where nobody has the full picture any more.

A defensible assessment of your architecture with a prioritised action list.

Process
Inventory, assessment against target architecture and regulation, prioritised actions, closing session.
Result
Report with prioritised actions, target architecture sketch, decision paper for management.

View in detail

Package 2

Project and sub-project management

For undertakings that need one accountable person – not another supplier.

One accountable person for plan, technology and communication.

Process
Scope agreement, planning and work packages, steering team and suppliers, status reporting, handover.
Result
defensible plan, status reports, accepted work packages, documented handover.

View in detail

Package 3

Interim: lead architect / platform operations lead

For vacancies that operations cannot wait for.

The role is filled while you recruit – evidenced by leading a platform team.

Process
Onboarding, technical leadership, weeklies, escalations, architecture decisions, orderly handover.
Result
running operations, decided architecture, documented handover.

View in detail

Package 4

AI architectures and automation

For organisations that must run AI in their own network – without cloud and without outside access.

Run AI in your own network and automate processes – compliant with your rules.

Process
Legal and requirements framing, hardware and platform decision, build and integration, tool assessment, operations handover.
Result
running model operations in your own network, documented operating processes, approved tools.

View in detail

Package 5

IT audit, DORA and ICT risk management

For financial entities and regulated organisations that must be audit-ready.

Become audit-ready: ICT risk management under Article 6 DORA, evidenced and traceable.

Process
Audit planning and scoping, review of the ICT risk management framework, register of information and contracts, findings and remediation tracking.
Result
audit report to IIA and DIIR standards, remediation plan with owners and dates, defensible evidence.

View in detail

Package 6

Training and seminars

For teams that should be able to do it themselves afterwards.

Your team can do it themselves afterwards – in IT, ITSM, project management, cloud, security and DORA.

Process
Tailoring to your environment, materials and practice environment, delivery using your own cases, wrap-up with proof of learning.
Result
trained team, reusable materials, exam preparation for ITIL, PRINCE2 or ISACA on request.

View in detail

Request an initial call Open the services as their own page

Case studies

Selected projects

Problem, approach, result – only what can be evidenced.

On-premise AI in a segregated network Opens the full case study in a window over this page. Escape closes it again.

Deutsche Telekom AG – Telekom Security – Berlin. Classified information network under VS-NfD.

Problem: AI tools and models are required but must not leave the segregated environment.

Approach: Planned the AI workload hardware (HP ProLiant Gen10), built and integrated on-premise LLM servers under VS-NfD operating rules, assessed and rolled out an adoption strategy for AI tools against BSI and data protection requirements, prompt engineering and Python-based tool integration.

Result: Model operations inside the own network without cloud dependency, documented adoption strategy, Python-based tool integration in production. Additionally an ELK stack SIEM with AI-assisted anomaly detection and automatic ticket creation in Jira.

View details Opens the full case study in a window over this page. Escape closes it again.

Closes the window. Escape does the same; focus returns to the link that opened it.

Case studies

On-premise AI in a segregated network

Deutsche Telekom AG – Telekom Security – Berlin. Classified information network under VS-NfD.

Problem

AI tools and models are required but must not leave the segregated environment.

Approach

Planned the AI workload hardware (HP ProLiant Gen10), built and integrated on-premise LLM servers under VS-NfD operating rules, assessed and rolled out an adoption strategy for AI tools against BSI and data protection requirements, prompt engineering and Python-based tool integration.

Result

Model operations inside the own network without cloud dependency, documented adoption strategy, Python-based tool integration in production. Additionally an ELK stack SIEM with AI-assisted anomaly detection and automatic ticket creation in Jira.

Project data

  • Client: Deutsche Telekom AG – Telekom Security
  • Role: Lead Systemarchitekt & Engineer · Fachleiter Plattformbetrieb
  • Period: 05/2025 – 08/2026
  • Location: Berlin
  • Working model: Vor Ort
  • Classification: VS-NfD

Request an initial call Open this case study as its own page
Active Directory consolidation Opens the full case study in a window over this page. Escape closes it again.

Goldfish IT – Project management and technical lead.

Problem: Several grown Active Directory domains with inconsistent permissions and unclear responsibilities.

Approach: Consolidation into a single forest using Quest On Demand Migration, migration of user accounts, group policies, resources and permissions under compliance rules – without interruption –, hardening measures, alignment with IT security and network teams, documentation and administrator training.

Result: consolidated directory, hardened configuration, trained administrators, documented migration path.

View details Opens the full case study in a window over this page. Escape closes it again.

Closes the window. Escape does the same; focus returns to the link that opened it.

Case studies

Active Directory consolidation

Goldfish IT – Project management and technical lead.

Problem

Several grown Active Directory domains with inconsistent permissions and unclear responsibilities.

Approach

Consolidation into a single forest using Quest On Demand Migration, migration of user accounts, group policies, resources and permissions under compliance rules – without interruption –, hardening measures, alignment with IT security and network teams, documentation and administrator training.

Result

consolidated directory, hardened configuration, trained administrators, documented migration path.

Project data

  • Client: Goldfish IT
  • Role: Projektleiter & technischer Lead · AD-Konsolidierung
  • Period: 09/2024 – 08/2026
  • Working model: Remote

Request an initial call Open this case study as its own page
Multi-cloud Kubernetes under BaFin, BSI and C5 rules Opens the full case study in a window over this page. Escape closes it again.

Atruvia AG and Siemens Financial Services – Two clients with the same architecture task.

Problem: A cloud architecture that gives business units their own room while keeping central compliance intact.

Approach: Hub-and-spoke concept with defined interfaces, Kubernetes clusters in a multi-cloud setup, Terraform and Ansible, CI/CD pipelines, ITSM build with CMDB, security and load testing, steering of external service providers.

Result: delivered cluster and automation platform, defined landing zone interfaces, compliance with BaFin, BSI and C5, documented handover.

View details Opens the full case study in a window over this page. Escape closes it again.

Closes the window. Escape does the same; focus returns to the link that opened it.

Case studies

Multi-cloud Kubernetes under BaFin, BSI and C5 rules

Atruvia AG and Siemens Financial Services – Two clients with the same architecture task.

Problem

A cloud architecture that gives business units their own room while keeping central compliance intact.

Approach

Hub-and-spoke concept with defined interfaces, Kubernetes clusters in a multi-cloud setup, Terraform and Ansible, CI/CD pipelines, ITSM build with CMDB, security and load testing, steering of external service providers.

Result

delivered cluster and automation platform, defined landing zone interfaces, compliance with BaFin, BSI and C5, documented handover.

Project data

  • Client: Atruvia AG
  • Role: Cloud Solutions Architect · Scrum Master · DevOps
  • Period: 02/2023 – 08/2023
  • Working model: Remote

Request an initial call Open this case study as its own page
Further projects

  • Bitmarck Service GmbH – AD concepts for tenant separation at statutory health insurers, PRINCE2 project management
  • Dataport – M365 rollout and identity management for municipal administration
  • SIT Südwestfalen IT – infrastructure modernisation, virtualisation, ITSM and service catalogue
  • 50Hertz Transmission GmbH – AI-assisted big data automation with Databricks and Azure ML
  • NGDA Apotheker Verband – e-prescription rollout, CI/CD and billing API
  • NXP Semiconductors – migration of 25 billion records into a multi-cloud environment

Client names are used only with approval. 17 projects are fully documented, 27 more in short form.

Starting point

Typical assignments

Six situations I have been brought into over the past years.

  • AI is required but must not run in the cloud.
  • IT operations cannot be steered: unclear tickets, missing metrics.
  • Security incidents surface too late; logs are not evaluated together.
  • The Active Directory landscape has grown: several domains, unclear permissions.
  • Infrastructure does not scale; virtualisation, storage and network grew apart.

  • Architecture and delivery are separated – the gap between them stays open.
How I work

How I work

Five steps, regardless of assignment size.

  1. 1

    Initial call, 30 minutes

    We assess the situation. You get an honest view on whether I am the right fit – including a no.

  2. 2

    Findings

    I look at documents, systems and operational reality. No remote judgement.

  3. 3

    Architecture decision

    Target architecture, options and effort in writing. You decide, not me.

  4. 4

    Delivery

    I build, steer or support – depending on the assignment. I stay reachable when it matters.

  5. 5

    Handover

    Documentation, training and a contact for what comes next.

About

Who works here

My name is Matthias Barth. I am an IT architect and have worked in infrastructure, operations and project management for over 25 years. I started in 1999 as a systems engineer; since then I have seen the disciplines from the inside: engineering, project management, service management, development.

What keeps me here: I want to understand how something works down to machine level – that started at 14 on a C64 and never stopped.

You work with me directly, not with a team. The contracting party is Bits and Friends GmbH, of which I am managing director – the consulting itself is done by me personally.

More about me

What sets me apart

I do not just deliver the target architecture, I stand behind its operation as well. That is why I regularly take responsibility for both at once – as lead architect and as project manager.

Request an initial call

How I work

Reliable, structured, to the point, solution-oriented – how I work is described on the About page.

I also teach IT, ITSM, project management, cloud, IT security, and DORA and ICT risk management – at institutes and in-house.

AI expertise Teaching and training

Evidence

Evidence instead of claims

CertificationsPRINCE2 – Practitioner & Trainer · ITIL V2/V3 – ServiceManager & Trainer · SCRUM Master – Zertifiziert
EducationMSc Computer Science · BSc Psychology
LanguagesDeutsch (muttersprache) · Englisch (verhandlungssicher) · Schwedisch (fließend) · Dänisch / Norwegisch (gutes verständnis)
Regulatory practiceVS-NfD · KRITIS and NIS2 · BSI IT baseline protection · ISO 27001 · BaFin and C5 · FINMA
Scope17 documented projects · 27 further projects (short form) · over 25 years in the field
Industriespublic administration · healthcare · finance · energy · industry · telecommunications

Service

IT audit, DORA and ICT risk management

For financial entities and regulated organisations that must be audit-ready.

Review of the ICT risk management framework under Article 6 DORA, register of information, contractual requirements and incident management – with an audit report to IIA and DIIR standards.

View in detail

Certifications and partnerships

  • Badge: Alliance for Cyber Security, Partner
    Alliance for Cyber Security Partner of the Alliance for Cyber Security, run by the German BSI.
  • Badge: DGQ quality management, ISO 9001:2015
    ISO 9001:2015 Quality management certified to ISO 9001:2015 (DGQ).
  • Badge: SecuryTi Trust Seal, made in Germany, TeleTrusT
    SecuryTi Trust Seal Trust Seal "made in Germany" of the TeleTrusT IT security association.

Contact

Request an initial call

Describe your situation in three sentences. I usually reply within one business day with an assessment and two time slots.

Required

Required. Used only to answer you.

Required. 20 to 4000 characters.

Required fields are marked with *.